
When pressure runs away or gas escapes, there is no time to wait for an operator to decide what to close. An independent, fail safe system detects the danger and drives the plant to a safe state within seconds.
Oil and gas platforms, refineries and chemical plants rely on dedicated safety systems that act when normal control fails. Shutdown logic, valves and blowdown work together to isolate inventory and remove energy.
What Is an Emergency Shutdown System?
An emergency shutdown system, or ESD, is an independent safety instrumented system that detects hazardous conditions and automatically isolates, depressurises or stops process equipment to bring the plant to a safe state. It is separate from the basic process control system, as explained in SIS and BPCS differences.
What Is Piping lists four core parts: dedicated transmitters, fail safe shutdown valves, logic solvers and blowdown valves. Plants usually define three or four shutdown levels ranked by criticality.
The ESD is designed and managed under IEC 61511, with each function assigned a safety integrity level. Oil and gas, nuclear, turbines, petrochemical plants and boilers all use it.
Everything is designed to fail safe. Loss of power, air or signal must move valves to their safe position.
4 Crucial ESD Levels
| Level | Scope | Typical Action |
|---|---|---|
| ESD 0 | Total facility, abandon | Shut everything, depressurise, isolate power |
| ESD 1 | Facility or platform | Isolate wells and export, blowdown |
| ESD 2 | Process area | Stop a section, isolate inventory |
| ESD 3 | Single unit or equipment | Trip one compressor or pump |
Higher levels always include the actions of lower ones. The exact naming varies between companies and sites.
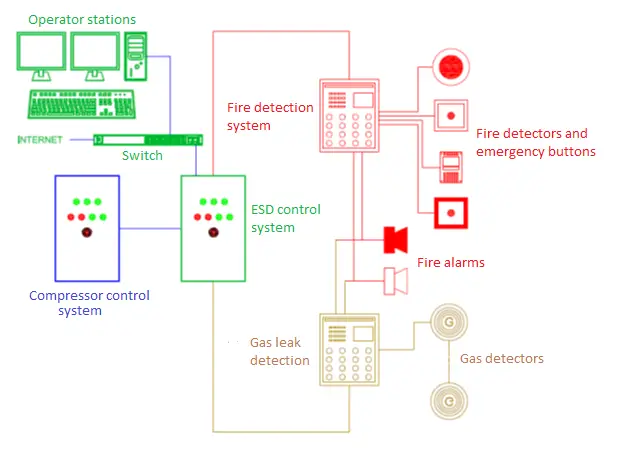
Fire and gas detection often triggers ESD levels automatically, while manual push buttons are provided at control rooms and escape routes.
Key Components
Dedicated pressure, level, temperature and gas transmitters.
Certified safety PLC with voting and diagnostics.
Fail closed isolation valves with solenoids.
Fail open valves to flare.
Final elements are often the weakest link, see SIS final element reliability. Valve positions on loss of air follow fail safe valve rules.
Logic solvers such as those described in Triconex PLC features use triple modular redundancy for high availability.
How a Trip Happens
Voting such as 2oo3 logic balances safety against spurious trips. Other schemes are compared in voting architectures.
De energise to trip design means the system fails toward safety whenever power or wiring is lost.
PFDavg Formula
RRF = 1 ÷ PFDavg
λDU = dangerous undetected failure rate per hour, TI = proof test interval in hours
Example:
λDU = 0.000002 per hour, or 2 failures per million hours
TI = 8760 h, PFDavg = 0.000002 × 8760 ÷ 2 = 0.00876
RRF ≈ 114, within the SIL 2 band
Shorter proof test intervals lower PFDavg, as covered in proof test interval and coverage. The target comes from LOPA or risk graphs.
Testing and Bypass Control
Every emergency shutdown system needs a written proof test procedure that trips each sensor, logic path and valve end to end. Records must show the as found and as left condition of every device.
Bypasses for maintenance must be authorised, time limited and visible on the operator console. A forgotten bypass is one of the most common causes of failed trips in incident reports.
PFDavg Calculator
This simple formula ignores common cause, diagnostics and test coverage. Use certified tools for final SIL verification.
- Independent from control systems.
- Fail safe, de energise to trip.
- Certified components.
- Regular proof testing.
- Stuck shutdown valves.
- Bypasses left in place.
- Shared sensors with control.
- Missed proof tests.
Manage the ESD through its whole life using the SIS safety lifecycle. High integrity pressure protection is a related layer, see HIPPS.
ESD Reliability Optimisation PDF
Oil and Gas ESD Video
Emergency Shutdown System FAQ
Related Articles
External References
- ESD Design Optimization, MATEC Web of Conferences
- ESD System, What Is Piping
- Safety Instrumented System, Wikipedia
What We Learn Today
- An emergency shutdown system acts independently to reach a safe state.
- Sensors, logic solvers, SDVs and BDVs form the core.
- Fail safe design, voting and proof testing set its reliability.