
Every override switch on a safety instrumented system is a deliberate hole punched through a layer of protection, useful during maintenance, dangerous the moment nobody remembers it is still open.
A Safety Signal Override temporarily disables a specific safety instrumented function so maintenance or a planned process condition can proceed without an unwanted trip, under strict authorization and logging controls.
Reading how a HAZOP study identifies protection layers first gives useful context, since an override always removes one of the very layers that study assumed would be available.
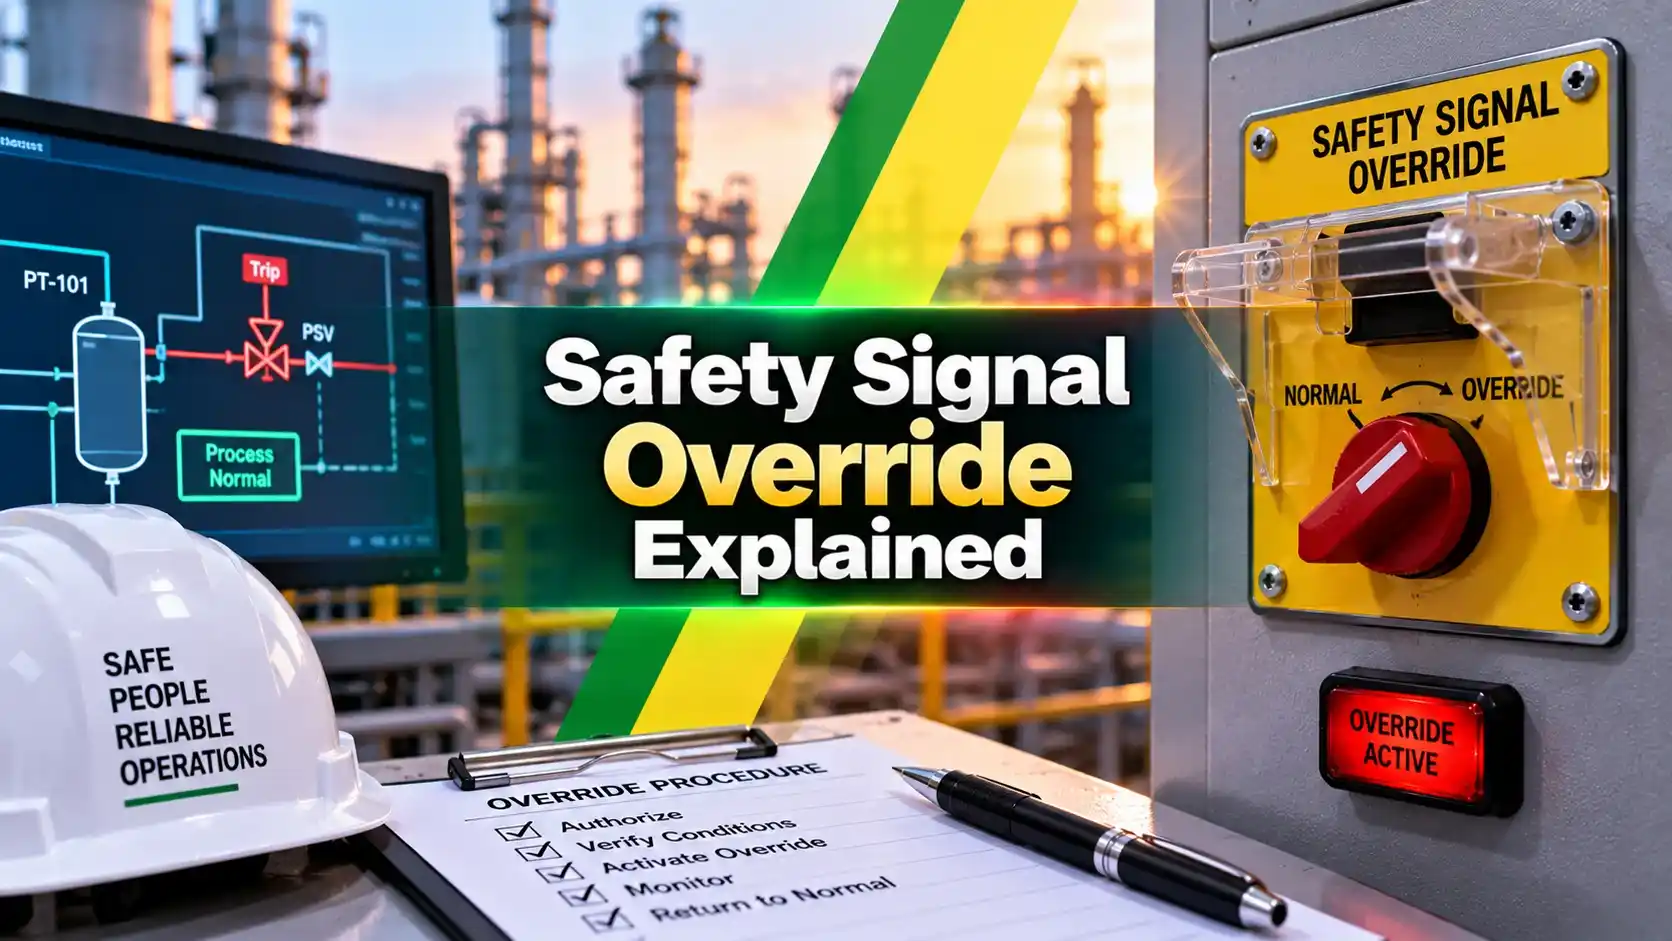
Safety Signal Override
A safety instrumented function normally trips a process to a safe state the instant a monitored condition crosses its set limit, with no operator judgment involved in that decision.
A Safety Signal Override intentionally disables that automatic trip for one specific signal, for a limited time, so a legitimate activity such as equipment repair or a planned startup sequence can proceed.
Because this removes real protection, every override is governed by IEC 61511 requirements covering authorization, time limits, alarm indication, and detailed logging of who applied it and why.
Maintenance Override vs Process Override
A Maintenance Override Switch, usually shortened to MOS, is applied while a specific sensor or final element is out of service for repair, calibration, or proof testing.
A Process Override Switch, shortened to POS, is applied during a defined process condition, such as a startup sequence, where the safety function's normal trip point would otherwise be met by a known, temporary, and accepted condition.
Both switches exist specifically so an override is applied through a controlled, auditable mechanism rather than through an ad hoc change buried inside program logic.
Key Concepts Behind a Safety Signal Override
| Property | Maintenance Override (MOS) | Process Override (POS) |
|---|---|---|
| Typical trigger | Device out of service for repair or proof test | Known, accepted process condition such as startup |
| Duration | Held until maintenance work is complete | Usually auto clears after a set time or condition |
| Voting logic impact | Can degrade the voting group's redundancy | Applied against a specific expected process state |
Controls Every Override Must Have
Where Overrides Show Up in Real Operations
Common Mistakes With Safety Overrides
The Full Lifecycle of an Override
A properly managed override starts well before the key is ever turned, with a written request identifying the specific signal, the reason, the expected duration, and the person accountable for it.
Once approved, the override is applied through its dedicated switch, the operator display immediately shows a persistent alarm, and the event is timestamped in the plant's electronic log automatically.
Throughout the override period, a compensating measure, whether extra operator rounds, a temporary manual check, or an alternate instrument reading, keeps some form of protection in place for that specific hazard.
Closing the override out is not automatic in every design, someone with authorization confirms the original condition no longer applies before the switch is returned to its normal position.
Auditing Override History
Reviewing override logs on a regular schedule, not just after an incident, reveals patterns such as one signal being overridden repeatedly, which usually points to an underlying reliability problem worth fixing at the source.
A signal that needs overriding every few weeks because of nuisance trips is a design or maintenance issue disguised as routine practice, and treating the symptom indefinitely eventually erodes the whole safety culture around overrides.
Many sites set a target for total active override count and total override duration across the plant, tracking both as a leading indicator of safety system health rather than waiting for a near miss to notice a trend.
Voting Architecture and Override Rules
A two out of three voting group can tolerate one channel being taken out of the vote while the remaining two still provide valid protection, which is why a negative override is often acceptable there.
A one out of two voting group loses meaningful redundancy the instant one channel is overridden, so stricter conditions, such as continuous operator monitoring or a backup reading, are typically required before that override proceeds.
Understanding a specific safety function's exact voting architecture before authorizing an override is not optional paperwork, it is the actual technical basis for whether that override is safe to apply at all.
Override vs Leaving the Signal Alone
With a Controlled Override
Maintenance or startup can proceed on schedule, with logging and alarms keeping the risk visible and time bound.
Without an Override
A nuisance trip may occur repeatedly during known, accepted conditions, though full protection stays continuously active.
The right answer is never to avoid overrides entirely, it is to make sure every override that does occur is authorized, visible, time bound, and properly closed out.
How Modern DCS and SIS Platforms Display Overrides
Older hardwired panels showed override status through a single lit indicator lamp next to the affected switch, easy to miss on a busy console during a shift change.
Modern integrated DCS and SIS platforms surface every active override directly on the process graphic where the operator is already looking, often with a distinct color and a running timer showing elapsed duration.
Some platforms add a dedicated summary screen listing every active override across the entire unit, letting a shift supervisor see the full protection picture in one glance rather than hunting across individual graphics.
Exportable Records for Compliance
Regulatory audits and internal safety reviews both expect a clear, exportable record of override history, not a verbal account pieced together from memory or scattered paper logs.
A platform that timestamps every override event, records the responsible person, and exports that history to a standard report format turns what used to be a manual reconciliation task into a routine query.
This record also supports incident investigation directly, since knowing exactly which protections were active, and which were overridden, at the moment of an event is often the first fact investigators need.
Watch: MOS and POS Explained
Safety Signal Override FAQs
None of this makes an override safe on its own, discipline around authorization, alarms, logging, and closing out each instance promptly is what actually keeps a plant protected while maintenance and startup activities continue.
Related Articles on This Site
- HAZOP Study Explained
- What Is SIL, Safety Integrity Level
- Safety Instrumented Function SIF Design
- SIS Final Element Reliability
- Process Safety vs Functional Safety
External References
What We Learn Today
- A safety signal override temporarily disables one function, always under strict authorization and logging rules.
- Maintenance overrides cover device repair, process overrides cover known, temporary process conditions like startup.
- Every override needs a compensating measure and a clear path to being closed out promptly.