
A plant network full of old controllers and unpatched Windows stations hides weaknesses that attackers love to find first. Finding them safely, ranking them by real process risk and fixing the worst ones first is the heart of good OT defense.
Industrial systems cannot be scanned and patched the way office computers are, because a careless probe can stop a controller. A structured assessment finds weaknesses safely and ranks them by process consequence.
What Is an OT Vulnerability Assessment?
An OT vulnerability assessment is a structured process to find, verify and rank security weaknesses in industrial control systems such as PLCs, DCS nodes, HMIs and network devices. It considers the effect on the physical process, not only on data, and maps findings to the Purdue model levels.
Weaknesses include missing patches, default or hardcoded passwords, open services and insecure protocols. Misconfigured firewalls and flat networks are just as common.
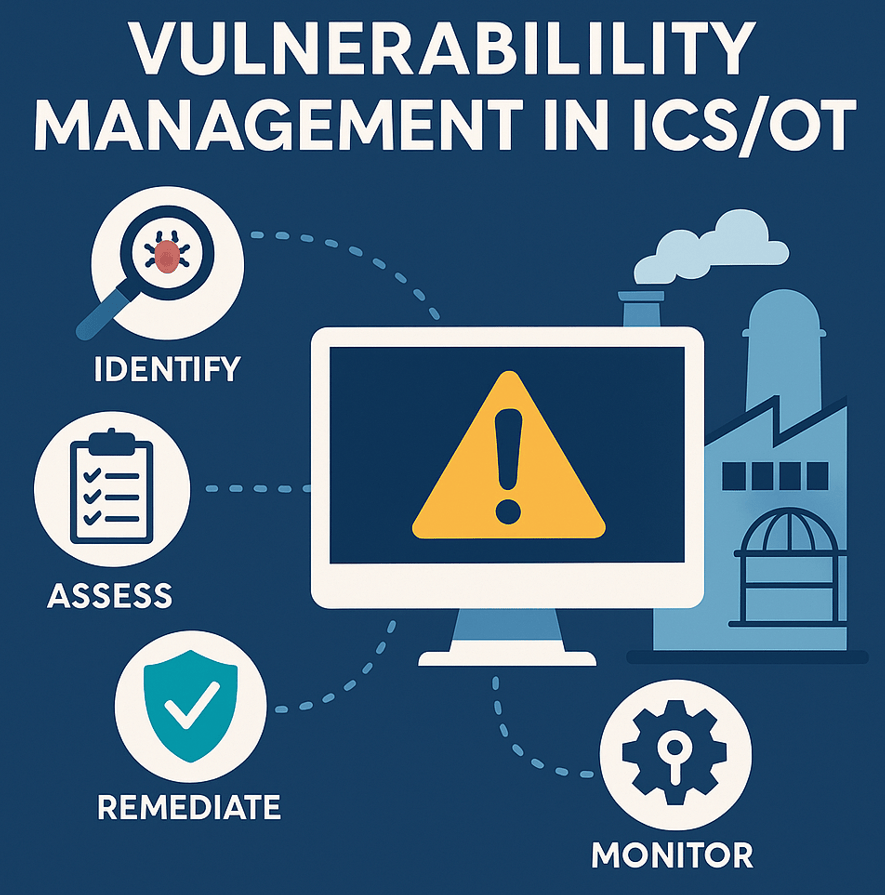
The Electrical Engineering Center notes that many OT systems still run Windows XP with hardcoded passwords. It also reports that OT is patched quarterly or yearly, compared with weekly or monthly in IT.
Stuxnet, Triton and BlackEnergy all exploited unpatched ICS weaknesses, according to the same source. These incidents are summarised in types of cyber attacks.
Why OT Needs a Different Approach
| Aspect | IT Assessment | OT Assessment |
|---|---|---|
| Top priority | Confidentiality | Safety and availability |
| Scanning | Frequent active scans | Mostly passive, active only with care |
| Patch cycle | Weekly or monthly | Quarterly, yearly or at shutdowns |
| Asset life | 3 to 5 years | 15 to 25 years |
| Failure impact | Data loss | Process upset or harm |
Controllers with small network stacks can crash when probed with unexpected traffic. That is why the IEC 62443 and NIST approaches treat testing as a planned activity.
Passive and Active Scanning Precautions
Listens to a SPAN or tap copy of traffic without sending packets.
Sends probes to discover services and versions.
Reads firmware, settings and logs offline.
NIST SP 800 82 Rev 3 advises that active scanning should be tried first on a test system or a lab copy. When used on live systems, it should be coordinated with operations and the vendor.
Passive tools build an asset list and flag weak protocols with no risk to the process. Good segmentation, explained in air gapped vs segmented networks, also limits scan scope.
6 Steps of an OT Vulnerability Assessment
A complete asset inventory is the base of everything else. Old platforms found here often feed obsolescence planning.
Vendor advisories must be checked before any patch, because many ICS vendors approve updates only after testing. Some fixes wait until the next shutdown.
Scoring with CVSS and CISA KEV
CVSS gives each vulnerability a base score from 0 to 10 based on attack vector, complexity and impact. It does not know how important the asset is to your process.
The CISA Known Exploited Vulnerabilities catalog lists flaws already used in real attacks. Any match on a reachable asset deserves fast action.
Risk score = CVSS × Asset criticality × Exposure factor
Criticality 1 to 5, exposure 1 isolated, 2 plant network, 3 remote access
Example:
CVSS 7.5, criticality 4, exposure 2
Risk score = 7.5 × 4 × 2 = 60.0 of 150
Priority 2, fix at the next planned outage
This simple weighting is a planning aid, not a standard method. Adjust the weights to your own risk matrix.
Risk Priority Calculator
Raise the priority of any item listed in CISA KEV, whatever its score. Record the reason for every decision.
Benefits and Limits
- Finds weaknesses before attackers do.
- Focuses budget on real process risk.
- Supports IEC 62443 compliance.
- Builds an accurate asset inventory.
- Active probes can upset old devices.
- Patches often wait for shutdowns.
- Results age quickly without repeats.
- Needs skilled OT and IT staff.
Where patching is impossible, use compensating controls from the SCADA security checklist and network security guides. Firewall rules and allowlisting reduce exposure fast.
Repeat the OT vulnerability assessment at least yearly and after major changes. Tie results to PLC cybersecurity standards and zero trust design.
NIST Guide to OT Security PDF
OT Vulnerability Challenges Video
For hands on learning, try the courses listed in free OT cybersecurity training.
OT Vulnerability Assessment FAQ
Related Articles
- Purdue Model for ICS Security
- IEC 62443 Zones and Conduits
- SCADA Security Checklist
- Air Gapped vs Segmented ICS Networks
- Types of Cyber Attacks
External References
- NIST SP 800 82 Rev 3, Guide to OT Security
- Vulnerability Management in ICS and OT, Electrical Engineering Center
- Vulnerability Assessment, Wikipedia
What We Learn Today
- An OT vulnerability assessment ranks weaknesses by process risk.
- Passive monitoring is safest, active scans need careful planning.
- CVSS, CISA KEV and asset criticality guide remediation order.